Developer SDK: Zero-Egress Node.js & Browser PII Sanitization for AI Pipelines
In-process Node.js, WASM & Browser PII sanitization engine. Pre-emptively intercept sensitive customer data and secrets in <0.4ms local RAM before OpenAI, Anthropic, LangChain, or Vector DB ingestion.
npm i @privacyscrubber/sdk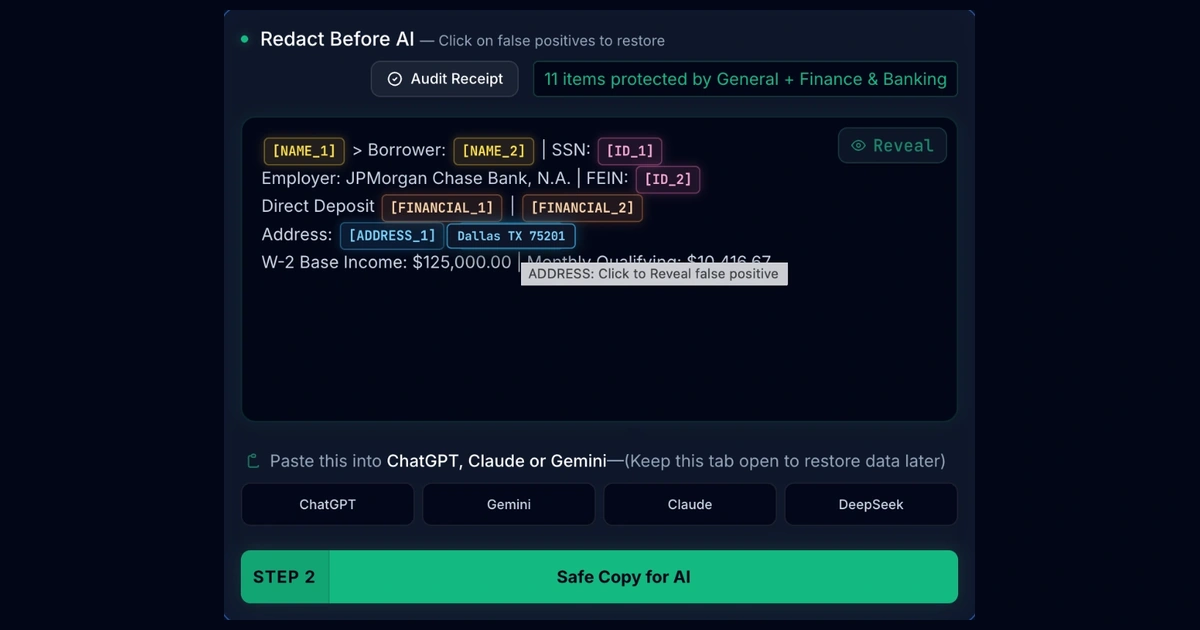

@privacyscrubber/sdk is a PII redaction SDK for Node.js, TypeScript, and the browser. It swaps names, emails, IDs, and API keys for placeholders like [NAME_1] on your own servers in under a millisecond, then puts the real values back into the AI reply. Nothing is sent to PrivacyScrubber or a cloud DLP service, and it ships with 30 industry profiles and drop-in OpenAI and Anthropic wrappers.
PII Redaction SDK: Live REPL & Latency Benchmark
Execute sub-millisecond in-memory sanitization live in your browser. Verify zero network egress, test bidirectional token detokenization, and inspect the volatile token map in real time across the 5 core scenarios.
npm i @privacyscrubber/sdkThe 5 Core Implementation Scenarios: Zero Data Loss Across Modern AI Stacks
From real-time streaming LLM prompts to complex JSON data lakes, tabular CSV files, and multimodal vision payloads.
Interactive Browser Sandbox (Case 5)Live Website Form & CRM Dual-Envelope InterceptorExpand Sandbox
Interactive Website Form Sandbox: Live In-Browser Interception
Test how PrivacyScrubber intercepts customer inquiries, support tickets, and contact form submissions inside the browser DOM before network transmission. Zero PII hits your public CRM or AI models.
<!-- 1-Line Browser Form Interceptor -->
<script type="module">
  import { sanitize } from 'https://cdn.jsdelivr.net/npm/@privacyscrubber/sdk@2.5.1/browser.js';

  document.querySelector('#support-form').addEventListener('submit', async (e) => {
    e.preventDefault();
    const textarea = e.target.querySelector('textarea');

    // 1. Sanitize in local browser RAM (<0.4ms)
    const { scrubbedText, tokenMap } = sanitize(textarea.value, { profile: 'support' });

    // 2. Dual-Envelope Dispatch:
    // Envelope A (Public CRM / AI): Transmit strictly safe tokens (0 PII)
    await fetch('/api/public-tickets', {
      method: 'POST',
      headers: { 'Content-Type': 'application/json' },
      body: JSON.stringify({ message: scrubbedText })
    });
    // Envelope B (Private Vault): Store encrypted tokenMap for staff review
    await secureVault.storeSession(ticketId, tokenMap);
  });
</script> 1. Zero Data Loss (Dual-Envelope)
Public CRM receives tokenized message ([EMAIL_1], [PHONE_1]), while your private vault holds the encrypted tokenMap. Authorized agents click "Reveal" to view real contact info.
2. Defense-in-Depth (No Bypass)
Never rely solely on browser JS. The same @privacyscrubber/sdk runs as a 1-line middleware on your Node.js or Next.js backend. If an adversary bypasses the form via cURL, the backend enforces sanitization.
3. Zero Client-Side Secret Leaks
The browser package requires zero private API keys on the frontend. Production quotas and commercial validation are handled at your private backend API gateway ($299/mo Developer SDK license).
Enterprise Architecture & Rollout5-Sprint Implementation Roadmap, 4 Strategic Pillars & Data-Flow LifecycleExpand Blueprint
Enterprise Implementation Roadmap: 5 Sprints to Zero-Trust Compliance
Designed for engineering leads, DevSecOps architects, and CISOs deploying generative AI across regulated workflows. A deterministic 5-stage sprint structure that eliminates vendor subprocessor friction, satisfies statutory compliance mandates, and ensures sub-millisecond execution.
Problem Solved: Prevents accidental leaks of customer names, email addresses, phone numbers, and employee credentials into ChatGPT, Claude, or internal copilot prompts.
Implementation: Drop wrapOpenAI() into backend API gateways or deploy @privacyscrubber/sdk/browser into Next.js App Router client components. Inbound prompts are tokenized before cloud transit; incoming assistant replies are restored deterministically in RAM.
Problem Solved: Eliminates irreversible vector poisoning. Embedding raw customer PII bakes personal data permanently into high-dimensional vector graphs, making individual deletion mathematically impossible without expensive full re-indexing.
Implementation: Embed sanitizeObject() into document chunking pipelines before feeding embedding models (Pinecone, Qdrant, Chroma). Store tokenMap in local customer-controlled KMS. Right-to-be-forgotten deletion triggers in O(1) constant time with $0 re-indexing cost.
Problem Solved: Protects tabular financial balance sheets, CSV rosters, and Zendesk/Jira support dumps from exposing credit card PANs, IBANs, and employee salaries to cloud analytics.
Implementation: Run chunked async stream transforms across 30 specialized industry profiles. Structural boundaries (commas, newlines, markdown table cells) remain 100% intact, enabling downstream LLM SQL generators and data analysts to operate without data corruption.
Problem Solved: Prevents visual leaks in document image processing. Uploading scanned identity cards, passports, and medical forms to multimodal models (GPT and Claude vision models) bypasses standard text-only DLP filters.
Implementation: Pre-extract text using local offline ZTDS™ OCR WASM; scrub national identifiers (Teudat Zehut, NHS, SIN, TFN) using deterministic structural verification; forward only sanitized bounding box tokens to vision reasoning engines.
Problem Solved: Eliminates developer credential drift, uncommitted secrets in Git, and provides verifiable compliance proofs for enterprise security audits without third-party vendor subprocessors.
Implementation: Deploy ps-guard in pre-commit hooks to block raw secrets. Use formatAuditReceipt() to export cryptographic receipts mapping every masked entity to statutory regulations with zero telemetry phone-home calls.
The 4 Strategic Pillars of In-Process Consumer Privacy
Modern SaaS engineering and AI applications bear strict legal and fiduciary responsibility for end-user data under GDPR, CCPA/CPRA, and global privacy statutes. Routing raw customer records through cloud DLP proxies only transfers liability to another third party while introducing latency and fragile network dependencies. The PrivacyScrubber Developer SDK operates as an autonomous consumer data fiduciary directly inside your runtime boundary:
Active Consumer Privacy Defense
Systematically enforces privacy rights on behalf of end-users at the application boundary. Sensitive identifiers are protected by default without relying on end-user configuration or manual user opt-ins.
Pre-Emptive Interception
Intercepts and quashes customer PII and infrastructure secrets before ingestion into vector databases, logging pipelines, or LLM inference engines—preventing irreversible compliance debt at the perimeter.
Zero Data Loss
Reversible, syntax-preserving deterministic tokens ([NAME_1], [FINANCIAL_1]) preserve 100% LLM reasoning fidelity. Real values are restored exclusively in local RAM with zero loss of downstream analytical utility.
Zero Third Parties
100% in-process execution inside your Node.js or browser memory. Completely eliminates third-party cloud DLP proxies (Skyflow, Lakera, AWS Comprehend, Nightfall), extra vendor DPAs, network hops, and egress fees.
Zero-Trust SDK Architecture: In-Memory Lifecycle
<0.4ms In-Memory ExecutionThe SDK intercepts raw payloads at your application boundary, tokenizes all PII and infrastructure secrets in volatile RAM, and forwards safe tokens to external LLMs or vector databases. Responses are deterministically restored before reaching the user.
Empirical Performance Benchmarks
Node.js 22 LTS • Apple M-SeriesArchitecture Comparison: In-Process SDK vs. Cloud DLP Proxies
Why modern engineering organizations choose in-process ZTDS execution over network-bound cloud middleware.
| Evaluation Factor | Legacy Cloud Proxy DLP (Skyflow, Nightfall) | PrivacyScrubber Developer SDK |
|---|---|---|
| Execution Location | External SaaS cloud proxy (Untrusted network hop) | 100% In-Process Node.js / Browser RAM (0 egress) |
| Per-Prompt Latency | +250ms to +1,200ms network round-trip | <0.4ms linear in-memory execution |
| GDPR Art. 17 Erasure | Requires full vector re-indexing ($14,200+ compute) | O(1) constant-time KMS session key purge ($0) |
| Subprocessor Liability | Adds vendor to compliance perimeter (6-8 wk review) | Zero Subprocessor: No third-party data processor formed |
| Commercial Pricing | $15–$45 / user / mo seat tax + volume egress | $299/mo flat for unlimited backend nodes & RAG lakes |
Calculate Your Monthly Savings & Latency Eliminated
Estimate savings from replacing cloud proxy DLP with local in-memory execution.
Production Integration Snippets: OpenAI, Anthropic, LangChain & LlamaIndex
Drop-in client wrappers and middleware interceptors. Sub-millisecond in-memory execution (<0.4ms) with zero third-party subprocessors.
// 1. Install zero-dependency SDK: npm i @privacyscrubber/sdk openai
import OpenAI from 'openai';
import { wrapOpenAI } from '@privacyscrubber/sdk';

// 2. Wrap client: In-process consumer data fiduciary (<0.4ms RAM execution)
// Flat $299/mo SDK license: Unlimited production microservices & 0 bytes cloud egress
const openai = wrapOpenAI(new OpenAI({ apiKey: process.env.OPENAI_API_KEY }), {
  profile: 'legal',          // 30 industry profiles (dev, medical, finance, etc.)
  detectSecrets: true,       // Intercepts AWS keys, Bearer JWTs, and database URIs
  licenseKey: process.env.PRIVACYSCRUBBER_KEY // Air-gapped Ed25519 (0 phone-home pings)
});

// 3. Standard OpenAI syntax: prompts are intercepted & tokenized in local memory before egress.
// Responses are automatically detokenized in RAM before returning to your caller.
const stream = await openai.chat.completions.create({
  model: process.env.OPENAI_MODEL,
  messages: [{
    role: 'user',
    content: 'Review contract for Johnathan Vance (SSN: 219-44-8891, email: jvance@acme.corp).'
  }],
  stream: true // StreamingDetokenizer buffers token boundaries across chunk fragments
});

for await (const chunk of stream) {
  process.stdout.write(chunk.choices[0]?.delta?.content || '');
}Procurement & Compliance Clearance48-Hour InfoSec Sign-Off, Dual-Key Architecture & A4 Conformance CertificateExpand Procurement Pack
From 6-Month InfoSec Review to 48-Hour Sign-Off
Enterprise buyers refuse to send confidential records and PII to frontier AI clouds. Combining in-process @privacyscrubber/sdk tokenization with public ZTDS.ai accreditation turns compliance from a sales blocker into an unfair conversion advantage.
Unlock Enterprise Deals
Shorten 3–6 month vendor risk reviews (SIG Lite, CAIQ, SOC 2 questionnaires). Provide the official A4 Conformance Certificate and verified registry listing proving zero customer PII leaves your infrastructure.
Statutory Risk Safe Harbor
Technical & organizational measures (TOMs) under GDPR Art. 32 and Israel PPL Amendment 13 Sec. 17. RAM-only sanitization physically prevents direct PII egress and eliminates officer personal administrative liability.
Zero-Risk AI Adoption
Query ChatGPT, Claude, and Gemini with confidential client records, contracts, and financial workpapers. Work safely in 100% Airplane Mode with 1-click deterministic reverse token re-hydration in local RAM.
The Dual-Key System: Technical Runtime vs. Public Trust
Subscribers receive two complementary cryptographic artifacts: a private in-process runtime key that unlocks unlimited throughput on your machines, and a public accreditation profile on ZTDS.ai that verifies compliance to prospective enterprise buyers.
In-Process Runtime Engine Key
- Format:
PS-SDK-[HEX]-[CHECKSUM](Ed25519 token) - Execution: 100% offline in RAM. Zero phone-home calls or external pings
- Capability: Unlocks unlimited characters and all 30 industry profiles
ZTDS Verified Registry Listing & A4 Cert
- Format: Public registry URL + printable A4 PDF Certificate of Conformance
- Verification: WebCrypto Ed25519 cryptographic signature verified by client CISOs
- Function: Ingested into Vanta, Drata, and enterprise security questionnaires
Official A4 Certificate of Conformance
Every production SDK deployment produces legally authoritative documentation. Export vector-crisp, printable A4 PDF certificates signed under the Zero-Trust Data Sanitization standard (ZTDS RFC v1.0) to satisfy enterprise customer security reviews, DPIAs, and statutory audits.
Ready for Immediate CISO & DPO Approval
Because the SDK executes 100% inside your local application runtime and transmits 0 bytes to PrivacyScrubber or third parties, PrivacyScrubber never receives your data, which typically keeps it outside GDPR Article 28 processor and HIPAA BAA scope (your counsel makes the final call). Review our pre-filled 40-Question Vendor Security Assessment (SIG Lite / CAIQ) and statutory Zero-Processor Safe Harbor Technical Pack. Your security team can verify zero network sockets using Wireshark or DevTools in under 60 seconds.
"Air-gapped Developer SDK for Node.js and WASM. Intercept PII in local RAM before LLM ingestion. Helps meet HIPAA Safe Harbor and SOC 2 controls."
Embeddable Node/WASM Guard for Developer SDK
Deploy reversible @privacyscrubber/sdk masking inside Node.js, TypeScript, and RAG chunkers at zero egress cost.
Frequently Asked Questions
Technical Details & Privacy Architecture
Can I embed the SDK directly into my website's HTML contact or support form?
What environments and runtimes does @privacyscrubber/sdk support?
How does the 1-line wrapOpenAI helper work?
How does the SDK protect Vector Databases (Pinecone, Chroma, Qdrant, Milvus, pgvector)?
How does the SDK handle multi-turn AI agents and state consistency?
Does the SDK detect infrastructure secrets and DevOps tokens?
What compliance frameworks and audit telemetry are generated?
Does the SDK require an outbound internet connection to validate licenses?
How does the SDK compare to MS Presidio and Google Cloud DLP?
Is the SDK fully typed with TypeScript?
How does pricing and quota management work for the Developer SDK, and is it free to try?
What is the difference between the technical SDK license key and the public ZTDS Certification listing?
Git Pre-Commit Leak Shield & 7-Day Evaluation Trial
Block leaked cloud credentials, API keys, database connection strings, and consumer PII before git commits leave developer workstations. Plus instant offline cryptographic evaluation trials.
Install the zero-dependency hook into .git/hooks/pre-commit. Scans staged diffs in <5ms and aborts commits if unmasked secrets are detected:
npx ps-git-guard uninstall Zero ConfigEvaluating in enterprise staging, ETL test environments, or PoC benchmarks? Generate a standalone cryptographic evaluation trial key directly from your terminal:
Deploy Zero-Trust PII Sanitization in Under 30 Seconds
Free with built-in quota for local dev & prototyping. Zero credit card. Zero account sign-up. Commercial license covers unlimited internal production nodes and RAG lakes.
npm i @privacyscrubber/sdk