
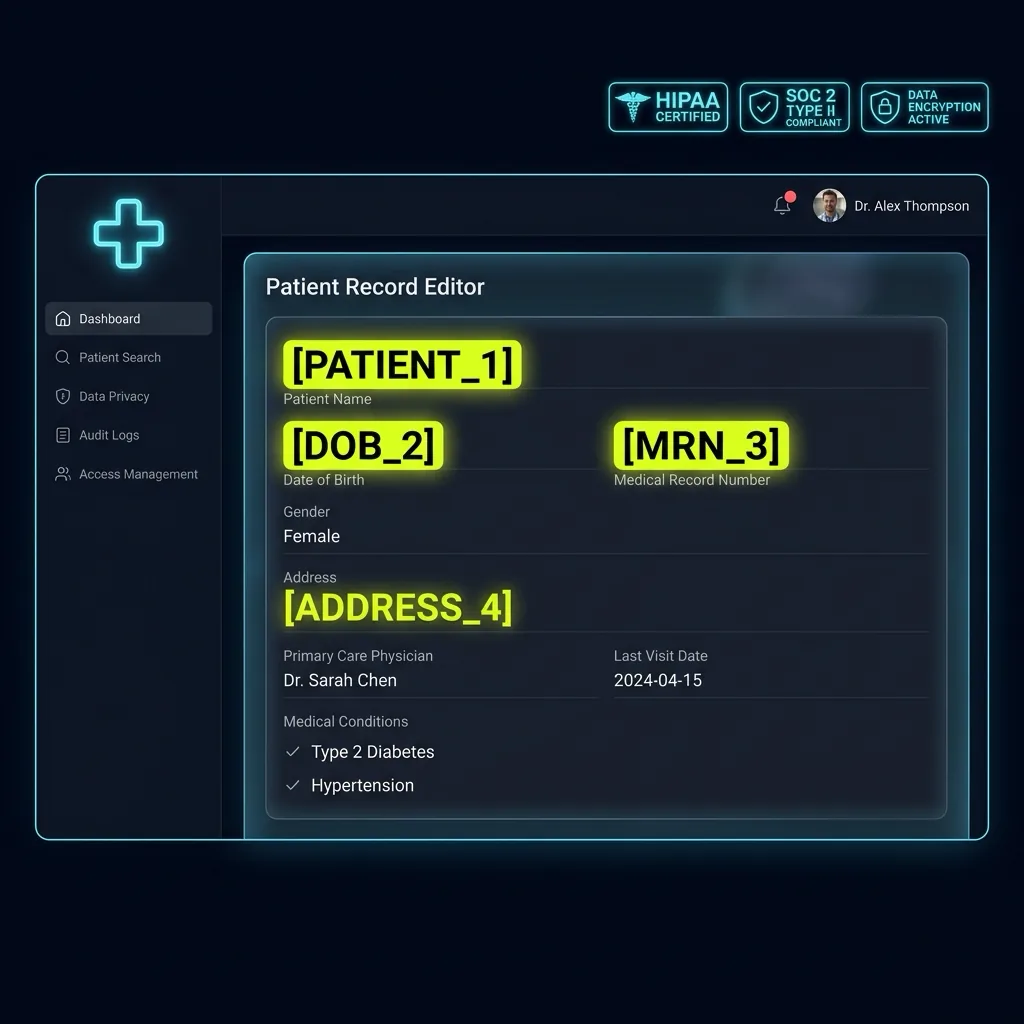
For medical governance over FDA AI Software Regulations and Patient PHI, and the Common Rule (45 CFR 46) for research involving human subjects audits inspect egress points. Tokenizing fda ai software phi via local RAM (medical) yields verifiable [PATIENT_1] isolation.
Threat Exposure Across FDA AI Software Regulations and Patient PHI
Why do healthcare administrators hit compliance friction around FDA AI Software Regulations and Patient PHI? Because ChatGPT retains fda ai software phi logs. Our Healthcare & Clinical AI privacy guides replace literals with [PATIENT_1] locally.
Why do network gateways miss FDA AI Software Regulations and Patient PHI? Understand FDA software validation and HIPAA Safe Harbor de-identification rules when integrating generative AI into health software. Encrypted browser prompts carrying fda ai software phi trigger raw hipaa compliant medical software ai retention beyond proxy inspection.
In-Memory Tokenization for hipaa compliant medical software ai
High-throughput FDA AI Software Regulations and Patient PHI pipelines break when hipaa compliant medical software ai hits third-party AI-assisted documentation platforms loggers. Installing local RAM (medical) strips sensitive fields into [NPI_1] inside local heap memory.
Zero containers or SaaS queues touch FDA AI Software Regulations and Patient PHI payloads: only anonymized [PATIENT_1] strings exit while fda guidelines patient privacy stays confidential on your machine.
Why Auditors Flag Raw Healthcare AI Prompts
Under and the Common Rule (45 CFR 46) for research involving human subjects, sending raw hipaa compliant medical software ai records to ChatGPT creates audit risk; safely protecting MRNs for AI details technical safe harbor inside local RAM.
Zero-Egress Tokenization for FDA AI Software Regulations and Patient PHI
Deploying offline endpoint scrubber traps FDA AI Software Regulations and Patient PHI inputs locally, mapping hipaa compliant medical software ai to [PATIENT_1]; aligned with anonymize patient ids in ecrf data for AI, ChatGPT never touches cleartext.
Test fda ai software phi scrubbing offline or run npx ztds-audit in CI: FDA AI Software Regulations and Patient PHI emits 0 bytes per LLM fine-tuning privacy.
Pre-Inference Redaction Matrix: FDA AI Software Regulations and Patient PHI
Before serializing FDA AI Software Regulations and Patient PHI payloads to external LLMs, PrivacyScrubber partitions every attribute into reversible RAM tokens versus preserved logic:
| Field Category | Directive | Token / State | Why It Matters for AI & Audit |
|---|---|---|---|
| Regulated Strings (zero-egress AI) | REDACT | [NPI_1] | Applies and the Common Rule (45 CFR 46) for research involving human subjects minimization locally before FDA AI Software Regulations and Patient PHI leaves RAM. |
| Tax, Token & Session Strings (hipaa compliant medical software ai) | REDACT | [MRN_1] | Zero-egress tokenization keeps FDA AI Software Regulations and Patient PHI identifiers off vendor storage. |
| Keys & Account Codes (hipaa compliant medical software ai) | REDACT | [MRN_1] | Stops hipaa compliant medical software ai credentials from entering cloud telemetry on FDA AI Software Regulations and Patient PHI. |
| and the Common Rule (45 CFR 46) for research involving human subjects Clause Taxonomy | PRESERVE | Cleartext Rules | Allows models to map FDA AI Software Regulations and Patient PHI findings directly against policy clauses. |
| Schema & Formatting (FDA AI Software Regulations and Patient PHI) | PRESERVE | Cleartext Structure | Keeps JSON, SQL, or prose syntax valid for ChatGPT on fda ai software phi. |
| Generic Roles & Category Tags | PRESERVE | Cleartext Roles | Provides operational context for FDA AI Software Regulations and Patient PHI while shielding real names. |
Ready-to-Use Sanitized Prompt: FDA AI Software Regulations and Patient PHI
Pair this structured instruction with your tokenized FDA AI Software Regulations and Patient PHI payload so ChatGPT, Claude, or Gemini preserves all bracketed surrogates for local RAM restoration:
Role: medical advisor evaluating FDA AI Software Regulations and Patient PHI.
Sanitized tokens ([PATIENT_1], [MRN_1]) mask all fda ai software phi identifiers.
1. Flag operational gaps in hipaa compliant medical software ai.
2. Recommend and the Common Rule (45 CFR 46) for research involving human subjects fixes.
3. Keep [PATIENT_1] unchanged.

[PASTE FDA AI SOFTWARE REGULATIONS AND PATIENT PHI TEXT]
Role: medical advisor evaluating FDA AI Software Regulations and Patient PHI.
Sanitized tokens ([PATIENT_1], [MRN_1]) mask all fda ai software phi identifiers.
1. Flag operational gaps in hipaa compliant medical software ai.
2. Recommend and the Common Rule (45 CFR 46) for research involving human subjects fixes.
3. Keep [PATIENT_1] unchanged.

[PASTE FDA AI SOFTWARE REGULATIONS AND PATIENT PHI TEXT]
