
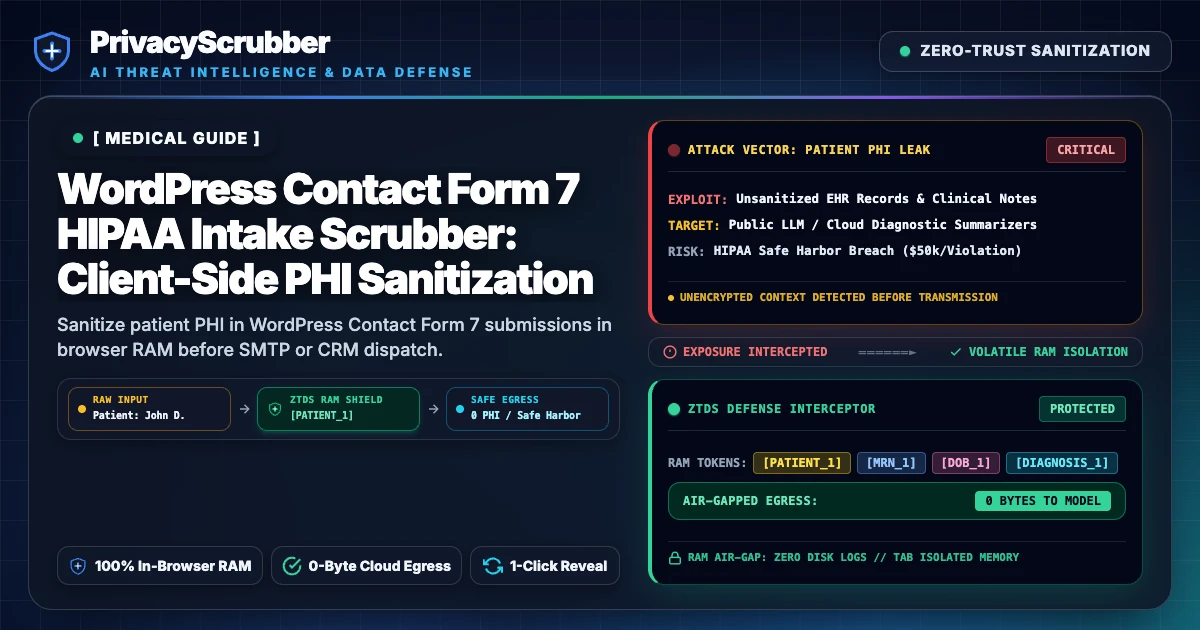
Standard WordPress installations running Contact Form 7 transmit raw patient names, dates of birth, medical record numbers, and clinical symptoms across unencrypted SMTP relays, shared MySQL tables (Flamingo), and third-party CRM webhooks without a Business Associate Agreement (BAA). Under 45 CFR § 164.514(b)(2) (HIPAA Safe Harbor) and the HIPAA Security Rule (§ 164.312(e)(1)), intercepting and tokenizing all 18 PHI categories inside the patient's browser DOM prior to form submission establishes a Technical Safe Harbor (Defense-in-Depth) so cleartext PHI never enters public email relays or AI triage agents.
What Healthcare Practitioners and Staff Send to AI During WordPress Contact Form 7 HIPAA Intake Scrubber
Safeguarding WordPress Contact Form 7 HIPAA Intake Scrubber is critical when medical researchers run ChatGPT. Unmasked contact form 7 hipaa compliance triggers and the Common Rule (45 CFR 46) for research involving human subjects egress gaps; our Healthcare & Clinical AI privacy guides explain local local RAM (Healthcare & Clinical) shielding.
For medical researchers, WordPress Contact Form 7 HIPAA Intake Scrubber mixes confidential wordpress hipaa patient intake form scrubber details that cannot leave custody. Sanitize patient PHI in WordPress Contact Form 7 submissions in browser RAM before SMTP or CRM dispatch. Zero BAA subprocessor risk with $99/mo TEAMS. Static rules fail without RAM interception.
Why Standard WordPress Contact Form 7 Setups Fail Healthcare Audits
When patients submit appointment requests, insurance policy numbers, or symptom descriptions through Contact Form 7, three immediate compliance bottlenecks arise under HIPAA Safe Harbor and Security Rule standards:
- Unencrypted SMTP & Email Relay Exposure: Contact Form 7 dispatches form fields via
wp_mail(). Even when TLS is enabled in transit, the message body rests in plaintext inside staff inboxes, IMAP caches, and third-party email relays that do not sign BAAs for raw clinical intake. - AI Receptionist & Webhook Leakage: Modern clinics connect Contact Form 7 to Zapier, Make, or LLM triage agents to classify urgency and draft responses. Forwarding raw patient narratives to cloud AI endpoints exposes direct identifiers to external model providers.
- Shared Hosting & Plugin Log Persistence: Form storage plugins and server access logs frequently capture raw POST payloads in plaintext MySQL tables. For broader clinical intake guidance, see protecting patient intake forms before AI processing.
Defense-in-Depth Architecture: Browser DOM Capture + Dual-Key Vault Isolation
The PrivacyScrubber WordPress ZTDS™ Form Guard (v2.5.0) enforces a two-layer zero-trust boundary:
Layer 1: Client-Side DOM Capture (<0.4ms)
Before Contact Form 7's AJAX serializer reads the form DOM, ztds-form-guard.js scans all text, email, tel, and textarea inputs in volatile browser RAM, replaces PHI with tokens ([NAME_1], [EMAIL_1], [PHONE_1], [SSN_1]), and writes the AES-256-GCM encrypted token dictionary into a hidden vault field.
Layer 2: Server-Side Dual-Key Re-Wrapping & Webhook Isolation
On the PHP backend (init priority 1), the plugin immediately strips _ztds_vault_payload from $_POST so third-party webhooks never receive the encrypted map, validates tokens, and re-encrypts the vault using an admin-only HMAC-SHA256 secret for the Built-In Encrypted Vault Inbox.
Field-by-Field Sanitization Rule for WordPress Contact Form 7 HIPAA Intake Scrubber
Before serializing WordPress Contact Form 7 HIPAA Intake Scrubber payloads to external LLMs, PrivacyScrubber partitions every attribute into reversible RAM tokens versus preserved logic:
| Document Field / Attribute | Action | RAM Surrogate | Statutory & Analytical Rationale |
|---|---|---|---|
| Routing Endpoints (sanitize phi contact form 7 before email) | REDACT | [DOB_1] | Blocks contact linkage when medical researchers analyze contact form 7 hipaa compliance batches. |
| Entity Names (Healthcare & Clinical) | REDACT | [PATIENT_1] | Maintains multi-turn coherence on contact form 7 hipaa compliance without exposing raw parties. |
| Subject Identifiers (contact form 7 hipaa compliance) | REDACT | [PATIENT_1] | and the Common Rule (45 CFR 46) for research involving human subjects guard prevents ChatGPT from retaining personal WordPress Contact Form 7 HIPAA Intake Scrubber records. |
| Severity Codes & Relative Sequence | PRESERVE | Cleartext Steps | Lets ChatGPT trace root causes cleanly inside sanitized wordpress hipaa patient intake form scrubber logs. |
| Non-PII Workflow Constraints | PRESERVE | Cleartext Context | Preserves reasoning constraints across WordPress Contact Form 7 HIPAA Intake Scrubber prompts sent offline. |
| Domain Instructions (Healthcare & Clinical) | PRESERVE | Cleartext Logic | Retains workflow intent so medical researchers get actionable sanitize phi contact form 7 before email outputs. |
Safe LLM Prompt Template for WordPress Contact Form 7 HIPAA Intake Scrubber
Pair this structured instruction with your tokenized WordPress Contact Form 7 HIPAA Intake Scrubber payload so ChatGPT, Claude, or Gemini preserves all bracketed surrogates for local RAM restoration:
Role: Healthcare & Clinical advisor evaluating WordPress Contact Form 7 HIPAA Intake Scrubber.
Sanitized tokens ([PATIENT_1], [MRN_1]) mask all contact form 7 hipaa compliance identifiers.
1. Flag operational gaps in wordpress hipaa patient intake form scrubber.
2. Recommend and the Common Rule (45 CFR 46) for research involving human subjects fixes.
3. Keep [PATIENT_1] unchanged.

[PASTE WORDPRESS CONTACT FORM 7 HIPAA INTAKE SCRUBBER TEXT]
Role: Healthcare & Clinical advisor evaluating WordPress Contact Form 7 HIPAA Intake Scrubber.
Sanitized tokens ([PATIENT_1], [MRN_1]) mask all contact form 7 hipaa compliance identifiers.
1. Flag operational gaps in wordpress hipaa patient intake form scrubber.
2. Recommend and the Common Rule (45 CFR 46) for research involving human subjects fixes.
3. Keep [PATIENT_1] unchanged.

[PASTE WORDPRESS CONTACT FORM 7 HIPAA INTAKE SCRUBBER TEXT]
Minimizing HIPAA Privacy Rule Exposure in WordPress Contact Form 7 HIPAA Intake Scrubber
Meeting and the Common Rule (45 CFR 46) for research involving human subjects data minimization during WordPress Contact Form 7 HIPAA Intake Scrubber leverages HIPAA fax document AI patterns to neutralize and the Common Rule (45 CFR 46) for research involving human subjects egress gaps via volatile [NPI_1] mapping.
Isolating Sensitive Fields Inside WordPress Contact Form 7 HIPAA Intake Scrubber Prompts
To avoid proxy lag on WordPress Contact Form 7 HIPAA Intake Scrubber, offline endpoint scrubber tokenizes contact form 7 hipaa compliance and wordpress hipaa patient intake form scrubber locally into [NPI_1] following AI marketing privacy.
Transparent DevTools inspection proves WordPress Contact Form 7 HIPAA Intake Scrubber sends zero contact form 7 hipaa compliance packets externally, backing Cursor MCP server security and and the Common Rule (45 CFR 46) for research involving human subjects.
