15,000 chars/scrub on General Profile, plus a 5,000-char trial across all 30 Specialized Profiles.
Scrub inside ChatGPT, Claude & Gemini (
Alt+Shift+X), plus free local dev quota in IDE MCP and Node SDK.Restore
[TYPE_N]tokens in local RAM and test single-file scrubbing (.pdf, .docx, .xlsx, plus 3 OCR scans).Built-in PCI credit cards, IBAN, SSN, emails, phones, IPv4/IPv6, and API secret key redaction in <2ms.
Zero servers and Airplane Mode verified, with live GDPR, HIPAA & SOC 2 risk scoring inside the workspace.
AI PII Redaction & Client-Side DLP for Prompts & DocumentsZero Cloud Egress. 100% RAM.
Sanitize sensitive customer PII, source code secrets, financial ledgers, and clinical records in local device RAM before sending to ChatGPT, Claude, Gemini, or Cursor. Supports GDPR Art. 32, HIPAA & SOC 2 technical safeguards with zero cloud proxies — interactive token:[FINANCIAL_DATA]
PII Sanitization Tool
Input
Tap to upload document or photoDrag & drop documents or photos
Sanitized in volatile RAM — zero data ever leaves your device.
Free tier: 1 file (up to 15k chars) · 100% in local RAM ·
Sanitize Before AI
Document Sanitizer Standby
Select a document or snap a photo above to strip PII instantly.
Sanitized locally in volatile RAM. Pre-prompt compliance maintained under GDPR & SOC 2.
Open in AI
General & GTM StackTokens active in RAM — click Reveal Original Data to auto-paste from clipboard & reveal.
"We run this before every ChatGPT session. Our InfoSec team was satisfied in one audit."
— Marcus T., Lead Compliance Engineer · European Fintech (400 employees)
"Finally — a PII tool that doesn't route my data through someone else's cloud."
— Jordan K., Senior DevOps Engineer · US Healthcare SaaS
"Used this to pass our SOC 2 AI-prompt review. The offline verification is the proof point."
— Priya N., Head of Legal Ops · Series B SaaS, 200 seats
Zero-Egress Security Proof100% Client RAM
Verify mathematical zero network transmission in Chrome DevTools or Airplane Mode
Why Enterprises & Developers Choose Client-Side AI PII Sanitization
Eliminate prompt leakage at the physical layer. Whether closing enterprise AI software contracts, shielding corporate officers from regulatory penalties, or protecting sensitive client workpapers.
Unlock Enterprise AI Deals
Stop losing high-ACV enterprise contracts to prospect InfoSec and DPO committees. Embed our zero-egress SDK into your AI workflows and arm sales teams with independent ZTDS Certificates of Conformance.
- Accelerate vendor InfoSec & DPO reviews with verifiable 0-byte egress
- Minimize subprocessor scope — direct PII is tokenized before cloud transmission
- Standalone in-process Node/WASM SDK with <1ms linear execution latency
Statutory Risk Minimization
Eliminate personal officer liability and statutory fines under GDPR Art. 83, EU AI Act, and CCPA/CPRA. Replace unenforceable employee guidelines with deterministic in-memory prompt tokenization.
- Proactive Technical & Organizational Measures (TOMs) under GDPR Art. 32
- 30 Specialized Profiles suppress narrative identifiers across tax, healthcare & legal
- Downloadable SHA-256 cryptographic compliance receipts for statutory audits
Zero-Risk AI Productivity
Process client tax returns, settlement transcripts, and confidential contracts in ChatGPT or Claude without breaching professional ethics, NDA agreements, or statutory confidentiality.
- 1-Click reverse de-tokenization restores original names and amounts in local RAM
- Operates fully offline in Airplane Mode — zero telemetry and zero server logs
- Visual PDF redaction & metadata purge for scanned tax and corporate filings
Sanitize High-Liability PDF, DOCX & Excel Documents
Before Submitting to Enterprise AI Models
Eliminate PII, PHI, financial ledgers, and trade secrets in local RAM. Select your document type below for verified field-by-field redaction matrices and safe AI prompts.
Finance, Underwriting & Banking
Prevent customer account numbers, SWIFT MT103 instructions, and payroll records from leaking into training corpora.
Legal Counsel & Court Discovery
Preserve attorney-client privilege under Federal Rule of Evidence 502. Neutralize case numbers and party names.
Healthcare & Life Sciences
Comply with HIPAA 45 CFR § 164.514 Safe Harbor. Mask MRNs, patient names, and dates while preserving clinical symptoms.
HR, Recruiting & Compensation
Conduct blind resume screening and salary benchmarking without injecting protected class identifiers or leaking payroll.
DevOps, Secrets & Autonomous AI Coding Agents
Protect internal API keys, database dumps, and cloud infrastructure secrets from entering LLM context windows in Cursor, Windsurf, Claude Code, and Copilot.
Zero-Metadata Engine Breakdown:
What PrivacyScrubber Strips Beyond Visible Text
Visual redaction alone leaves organizations exposed to court subpoenas and LLM data extraction. Real enterprise documents store deep internal XML structures, revision histories, and hidden text layers that cloud AI parsers automatically ingest.
3-Format Deep Dissection.DOCX / .XLSX XML.PDF Vector StreamOCR / EXIF PurgeInspect Format Internals
OpenXML Package Dissection
Word and Excel files are ZIP archives storing internal XML trees. Naive text deletion leaves metadata intact.
\\corp-nas\payroll). Vector Stream & Text Layer Erasure
Court discovery exhibits and medical records demand the Anti-Manafort standard: 0 underlying text traces.
Raster Burn-In & Hardware EXIF Purge
Mobile snapshots of driver licenses, invoices, and hospital intakes contain latent geolocation and hardware stamps.
CISO Verification MatrixAir-Gapped Standard ParityCompare 6 Vector Controls
| File Security Vector | Legacy / Cloud Redaction Tools | PrivacyScrubber ZTDS Engine |
|---|---|---|
| Visible PII Text (Names, SSNs, Accounts) | Replaced visually on screen | Replaced in-memory with reversible AI tokens or blackouts |
| Underlying PDF Text Layer (Anti-Manafort) | Retained under black rectangles (extractable by AI) | Physically destroyed from Tj/TJ vector streams |
| DOCX/XLSX Author & Company Metadata | Preserved in docProps/core.xml | Purged 100% prior to native file export |
| Track Changes & Deleted Comments | Stored in hidden XML revision tags | Completely stripped from ZIP container |
| Camera EXIF & Smartphone GPS Data | Kept in image headers, leaking coordinates | EXIF dropped, raster burned in on HTML5 Canvas |
| Network Egress & Server Storage | Uploaded to remote cloud proxy / API server | 0 bytes sent to network • 100% in local RAM (Airplane Mode) |
Direct File Format Engines (Zero Cloud Upload)
Cryptographic PII Audit Receipts & A4 Certificate of Conformance
Every deployed PrivacyScrubber engine produces legally authoritative documentation. Export vector-crisp, printable A4 PDF certificates signed under the Zero-Trust Data Sanitization standard (ZTDS RFC v1.0) to satisfy internal compliance audits, GDPR Data Protection Impact Assessments (DPIAs), and enterprise customer security reviews.
Client-Side RAM Sanitization vs. Cloud DLP Proxies:
Paper Promises vs Physical Data Sovereignty
Not your RAM, not your data. The fundamental divide between signing legal contracts to allocate post-breach liability versus enforcing mathematical zero-egress before generative models ever see raw text.
Model A: Cloud Paper Compliancevs.Model B: Physical Data Sovereignty (ZTDS™)Compare Architectural Models
Paper Compliance
Organizations rely on Data Processing Agreements (DPAs), Business Associate Agreements (BAAs), and trust declarations from cloud proxy vendors (Skyflow, Presidio Cloud, AWS Comprehend).
Continuous Third-Party Egress
Unredacted prompt text, client IDs, and financial records transit across external fiber cables to intermediary vendor cloud servers.
Residual Cloud Custody & Subpoena Risk
Ephemeral cloud caches, server crash logs, and worker heaps remain vulnerable to insider threats, infrastructure compromises, and CLOUD Act warrants.
Procurement Drag (6–8 Weeks)
Requires exhaustive InfoSec supplier questionnaires, subprocessor chain audits, and legal review of third-party indemnification caps.
Reactive Financial Exposure
When a cloud subprocessor leaks, the DPA only defines who pays the lawyers. Average IBM Cost of a Data Breach: $4.88M.
Physical Data Sovereignty
Organizations rely on deterministic CPU tokenization isolated in local workstation RAM (IETF draft-sibiryakov-ztds-protocol).
Strict Zero-Byte Network Transmission
Raw text never hits the network adapter. All tokenization, entity verification, and redactions complete inside browser V8 RAM in <2ms.
Physical Isolation Against Subpoena & Leaks
No cloud server holds your cleartext session map. It is mathematically impossible to breach, leak, or subpoena data that was never transmitted.
0-Day Procurement (GDPR Art. 28 Subprocessor Path Eliminated)
Because exactly 0.00 bytes of personal data leave client RAM, PrivacyScrubber is not a Data Processor under GDPR Art. 4(8) or HIPAA. InfoSec and Legal grant immediate clearance without 6-week vendor delays.
Empirical Verification (Airplane Mode)
Fully functional with Wi-Fi disabled. Inspect Chrome DevTools Network tab: exactly 0 requests and 0 bytes transferred.
Deep Zero-Metadata Office Sanitization
Beyond visible text, our in-RAM engine purges hidden XML properties (docProps/core.xml, wb.Props), wiping authors, corporate tags, and revision history in DOCX and XLSX before download.
Why Data Deletion from Frontier LLMs is Impossible
Once sensitive data enters an AI model or enterprise RAG vector store, it cannot be selectively deleted—machine unlearning remains unsolved. Network gateway DLPs miss encrypted WebSockets and streaming SSE tokens. PrivacyScrubber enforces source-level sanitization in local RAM before transmission, satisfying EU AI Act governance and DORA resilience mandates.
Sanitize AI Prompts Before They Leave Your Browser
In-Page Real-Time Protection on ChatGPT, Claude & Gemini
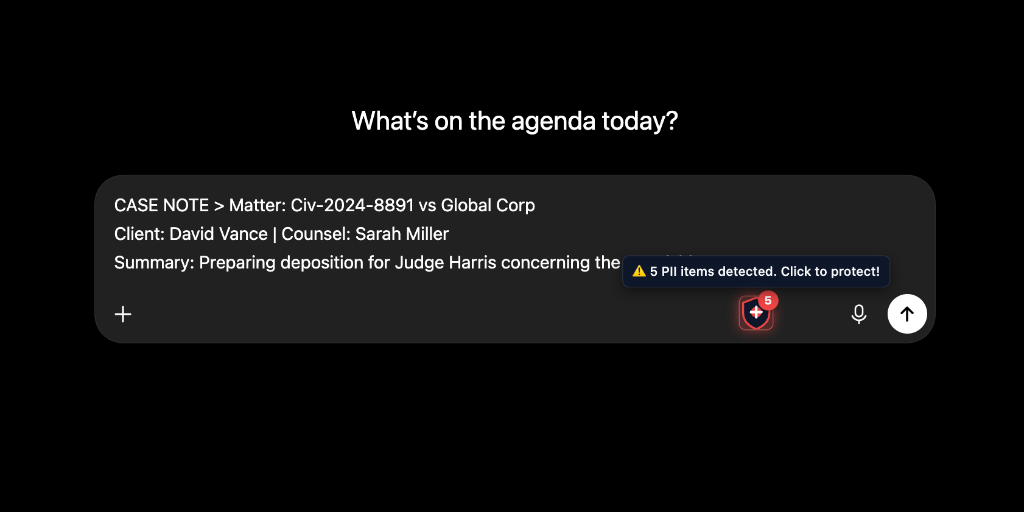
Automatically detect and tokenize customer names, API keys, medical notes, and financial data directly inside your AI chat window. 0ms network latency — 100% local browser RAM processing.
Zero-exfiltration prompt sanitization directly in your AI chat window
Intercepts names, emails, cards, and keys in local RAM before prompt transmission to LLMs. Zero server logs.
In-Page Prompt Sanitizer for ChatGPT, Claude & Gemini
Air-gapped client-side interception inside your AI text inputs. Customer identities, credentials, medical notes, and financial records are sanitized in local RAM before prompt transmission.
In-Page Auto-Detection (9 LLMs)
Native injectors for ChatGPT, Claude, Gemini, Copilot, DeepSeek, Perplexity, Poe, HuggingFace, and Mistral.
1-Click Reverse Reveal in Chat
Instantly swaps tokens in the AI response back to original names and data directly in your browser.
100% Offline RAM & ZTDS Receipts
30 industry profiles (HIPAA, GDPR), custom regex rules, and cryptographic audit receipts with zero server telemetry.

Step 1: Detection
Step 1 of 4Type or paste your text normally. The extension instantly detects sensitive data like names, emails, or IDs right inside the text box.
Verify Zero Data Egress in 60s & Technical Safeguards for
GDPR, HIPAA, SOC 2 & EU AI Act
No auditor or vendor trust needed. Open DevTools to prove PrivacyScrubber sends zero network requests with your data — backed by turnkey statutory compliance for enterprise LLM deployments.
60-Second Proof of Zero Transmission
Independent DevTools verification protocol for InfoSec & SecOps (0 requests · 0 B transferred)
Airplane Mode VerifiedInspect Steps
60-Second Proof of Zero Transmission
Independent DevTools verification protocol for InfoSec & SecOps (0 requests · 0 B transferred)
Press F12 or right-click → Inspect
Click the Clear icon to reset active request log
Cut Wi-Fi — engine runs 100% offline
Watch Network tab as text is tokenized
Zero bytes egressed to external endpoints — verified zero egress by architecture.
6 Tough Questions Security Architects Ask Us
Direct technical answers addressing the core questions evaluated by CISOs, security researchers, and enterprise review committees.
01Why not Presidio or cloud NER models?
02How is browser memory protected from extraction?
script-src 'self') with zero external scripts. The volatile ZTDS™ token dictionary is strictly tab-isolated, never stored on disk or cookies, and wiped on tab close. 03What happens if generative AI alters synthetic tokens?
04How does InfoSec audit compliance without central servers?
05Why use ZTDS if our enterprise signed an Azure OpenAI or ChatGPT Enterprise BAA?
06What if our documents contain rare or proprietary PII?
Architecture Benchmark Paper Contracts vs Technical Safeguards: Local RAM vs Cloud DLP
Sign a DPA to allocate liability after an incident, or isolate memory so a breach is physically impossible. Why enterprise security architects choose in-memory client-side ZTDS over cloud DLP proxies.
Compare Matrix
Paper Contracts vs Technical Safeguards: Local RAM vs Cloud DLP
Sign a DPA to allocate liability after an incident, or isolate memory so a breach is physically impossible. Why enterprise security architects choose in-memory client-side ZTDS over cloud DLP proxies.
Cloud DLP Proxies & Gateways
- Network Egress: Transmits unredacted prompt payloads over the internet to intermediate cloud proxy servers.
- High Latency: 250ms – 600ms latency penalty per AI query due to multi-tenant cloud roundtrips.
- Probabilistic NLP: Cloud LLM redactions risk hallucinating tokens, skipping entities, or rewriting prompt semantics.
- Procurement Overhead: Requires 6–8 week legal reviews, BAAs, DPAs, and third-party vendor risk questionnaires.
PrivacyScrubber Client-Side ZTDS
- 0-Byte Transmission: 100% volatile local RAM processing. Fully functional offline in Airplane Mode.
- Sub-2ms Latency: Near-zero latency overhead (<2ms local CPU tokenization). Zero network queues.
- Deterministic Precision: Rigorous deterministic pattern engines. Zero token hallucinations.
- Statutory Safe Harbor: Zero-processor architecture clears DPO reviews in 48 hours without third-party DPA gridlocks.
100% reproducible RAM tokenization
HIPAA Safe Harbor, GDPR, PCI DSS
Air-gapped scanned PDF processing
AI PII Redaction & Data Sanitization Pricing. Zero Per-Seat Tax.
Sanitize sensitive prompts, PDFs, and spreadsheets 100% locally in browser RAM before sending to ChatGPT, Claude, Gemini, or Cursor. Compare Free, PRO ($15/mo or $110 Lifetime), flat-rate Teams ($99/mo for unlimited seats), and in-process Node.js/WASM Developer SDK ($299/mo) plans — supporting GDPR Art. 32, HIPAA & SOC 2 technical safeguards with zero subprocessor risk.
Zero character limits across all 30 specialized profiles (HIPAA, Legal, Finance, W-2, Logs).
Unmetered in-page AI chat scrubbing plus air-gapped stdio MCP for Cursor, Windsurf & Claude.
Bulk-scrub 50+ files (.pdf, .docx, .xlsx, .csv) with zero-metadata XML purge and offline OCR.
Define custom regex and AES-256-GCM encrypted keyword rules for client names and project codes.
Download signed A4 cryptographic audit certificates proving zero raw PII egress per session.
Flat $99/mo license covers every employee across all 30 profiles with zero per-seat fees.
Share active token maps between colleagues via Argon2id + XChaCha20 encrypted
.ztdsbundles.Unlimited multi-file sanitization, vector PDF erasure, and offline WASM OCR across all staff.
Push locked custom rules (
.psblueprint) via Chrome GPO, Intune, or Jamf with key isolation.Downloadable A4 Conformance Certificates and pre-cleared CISO Safe Harbor memo to skip DPAs.
Unmetered headless Node.js & WASM scrubbing across all 30 profiles in backend containers & APIs.
Sanitize enterprise data before embedding into Pinecone, Qdrant, Weaviate, Chroma & LangChain.
Tokenize outbound LLM API payloads and rehydrate
[TYPE_N]surrogates in streaming responses.8.4 MB/s in-process throughput with programmatic custom rules, zero network hops, and 0 egress.
Public ztds.ai verification badge, programmatic SHA-256 receipts, and SDK CISO Safe Harbor memo.
AI Data Breach Cost vs. Cloud DLP vs. Client-Side ZTDS™ Pricing
Average cost of a GenAI corporate data breach according to the IBM Security Report.
- Up to €20M or 4% turnover (GDPR & EU AI Act Art. 50).
- $50,000/violation statutory HIPAA willful neglect fines.
- 6–12 week enterprise procurement stalling for vendor reviews.
Internal engineering salary to build, test and maintain custom regex DLP logic.
- $500–$2,000/mo server bills for centralized cloud proxy nodes.
- 200–500ms network roundtrip latency on every developer prompt.
- Ongoing regex drift, edge-case false positives & triage drag.
Flat-rate team protection with 100% in-memory client-side sanitization.
- 0-Day Approval: Zero subprocessors in the sanitization path, less DPA paperwork.
- <2ms local RAM execution with 0 bytes network egress.
- Turnkey compliance proofs: SOC 2 Type II & ISO 27001 mapping.
Offline Cryptographic Licensing: Zero Accounts & Air-Gapped Activation
We refuse to store your passwords or track your identity in a central database. Privacy is an engineering guarantee, not a marketing promise.
1. Zero Accounts & No Passwords
You never create an account, set a password, or trust us with login credentials. There is no cloud user database to be breached, scraped, or subpoenaed.
2. Offline Cryptographic Keys
Paid tiers (PRO, TEAMS, SDK) activate via an offline cryptographic license key. Validation occurs mathematically in your local RAM without cloud telemetry or pingbacks.
Traditional Cloud DLP vs. PrivacyScrubber TEAMS — 94% Cost Reduction
Cloud DLP vendors charge $30–$50/user/mo ($18,000–$30,000/yr for 50 seats), introduce 250ms+ network latency, and require months of vendor security assessments. PrivacyScrubber TEAMS costs $99/mo flat ($1,188/yr) for unlimited seats with zero server-side subprocessor liability.
Complete on-premise source code licensing, 100% air-gapped sovereign deployment, proprietary patent-pending architecture (U.S. & Int'l Patents Pending), custom SIEM log integration, dedicated GRC support & bilateral DPA for healthcare systems, banks, defense, and large multi-seat organizations.
What You Get & Why It MattersRole & feature entitlements across Free, PRO, TEAMS, and Enterprise tiers
Compare All Specifications →Hide Specifications ←
Role & feature entitlements across Free, PRO, TEAMS, and Enterprise tiers
Client-Side AI Privacy & PII Sanitization FAQ
Everything you need to know about browser-based PII redaction, compliance scope, and AI safety.
Security & ZTDSDoes PrivacyScrubber send my text, documents, or meeting transcripts to any server?
Security & ZTDSWhat is AI DLP and how does client-side browser sanitization differ from a legacy cloud proxy?
Compliance & LegalWhat is the AI data irreversibility problem and why must PII redaction happen at the client endpoint?
Security & ZTDSHow does PrivacyScrubber prevent data residue and protect browser heap memory?
script-src 'self') with zero third-party analytics prevents DOM and memory scraping. In-memory heap profiling enforces an ultra-lightweight ceiling under 6MB RAM (5.68 MB JS Heap) with sub-75ms streaming mutation scans. Security & ZTDSWhy deterministic regex rules instead of cloud NER models like Microsoft Presidio or BERT?
Compliance & LegalDoes PrivacyScrubber support HIPAA, GDPR, and SOC 2 de-identification?
Compliance & LegalWhy is a Data Processing Agreement (DPA) or BAA not required, and how does the CISO Memo bypass procurement delays?
Compliance & LegalWhy do organizations need ZTDS if they already have Azure OpenAI or ChatGPT Enterprise with a BAA?
Compliance & LegalHow does PrivacyScrubber protect enterprise RAG vector databases and prevent GDPR Article 17 re-indexing costs?
@privacyscrubber/sdk into your ingestion pipeline, raw PII is swapped with deterministic cryptographic tokens in Node.js heap (<0.065ms) before vector embedding. When an erasure request arrives, organizations simply purge the local key mapping, achieving instantaneous O(1) mathematical erasure at $0 infrastructure cost. Compliance & LegalHow can an enterprise CISO or SOC audit compliance without central servers?
Features & FilesHow does the Zero-Trust Agentic Guard work in practice when AI coding agents run shell commands or edit code?
Features & FilesCan PrivacyScrubber sanitize W-2 forms, paystubs, and payroll documents?
Features & FilesDoes PrivacyScrubber sanitize hidden document metadata (author, company name, revision history) in Word (DOCX) and Excel (XLSX) files?
docProps/core.xml and workbook properties. PrivacyScrubber's in-RAM sanitizer intercepts these archives in local browser memory, wipes original author and organization tags, eliminates custom metadata, and overwrites properties with anonymous synthetic signatures (PrivacyScrubber (Zero-Trust)) before export. Your exported files are completely clean both visibly and metadata-wise, with zero network transmission. Features & FilesWhat is the difference between AI Tokens mode and Blackout mode, and why do standard PDF blackout tools leak data?
Pricing & TeamsHow can solo coaches, therapists, and executive consultants sanitize client meeting transcripts (Zoom, Teams, Google Meet) without cloud exposure?
Pricing & TeamsWhat does the free Community version include?
@privacyscrubber/sdk) and IDE MCP Server (@privacyscrubber/mcp-server) with built-in session quotas — zero credit card, zero passwords, and zero accounts required. For solo practitioners and developers, you can also claim a 1-Year PRO Reviewer Pass ($180 value) 100% free with an honest review on G2. Pricing & TeamsWhat are the exact operational boundaries between Personal PRO, Team Workspace, and Developer SDK licenses?
Pricing & TeamsHow does TEAMS encrypted session handoff and decentralized administration work without a central database?
Pricing & TeamsCan I use PrivacyScrubber as an air-gapped MCP server in Cursor, Windsurf, or Claude Desktop, and is it free to use?
Pricing & TeamsIs there a developer SDK for backend Node.js and RAG pipelines, and how does it integrate out of the box?
Pricing & TeamsHow does PrivacyScrubber enable AI SaaS vendors to close enterprise deals and bypass 6-month InfoSec reviews?
Compliance & LegalWhat is the official A4 Certificate of Conformance and how do corporate auditors verify it?
ZTDS-CERT-2026-PRIVACYSCRUBBER-WEB-D02DC6). Corporate auditors, CISOs, and Data Protection Officers can independently inspect and verify our cryptographic invariants in real time at https://ztds.ai/verify/?target=privacyscrubber-web. The portal runs an offline Ed25519 signature validation directly in browser memory and generates an official, printable A4 Conformance Certificate. Procurement teams can download this signed PDF to attach directly to vendor risk assessments (SIG Lite, CAIQ) and statutory Technical and Organizational Measures (TOMs) dossiers under GDPR Art. 32. Pricing & TeamsHow does client-side in-RAM sanitization protect corporate directors, CISOs, and DPOs from personal liability under EU GDPR, EU AI Act, and CCPA/CPRA?
Need More Technical, Compliance, or Architecture Answers?
Explore our complete 45-question Knowledge Base covering HIPAA BAA exemptions, offline OCR raster flattening, Node.js SDK streaming, and air-gapped MCP stdio integration.
No matching questions found
Try searching for other keywords or reset the filter.
Compare Zero-Trust Alternatives
See how client-side RAM sanitization compares against cloud DLP proxies and server-side NLP models.
PrivacyScrubber vs Every Major PII Masking & AI DLP Tool
Compare PrivacyScrubber and ZTDS™ standard conformance side-by-side against 12 leading cloud DLP APIs, proxies, and SDKs...
PrivacyScrubber vs CamoText
Compare PrivacyScrubber vs CamoText for local AI data masking. Discover key differences in ChatGPT support, speed, and H...
PrivacyScrubber vs Justee AI
Compare PrivacyScrubber vs Justee AI. ZTDS™ local RAM execution eliminates cloud server transit risk for enterprise Chat...
Need CISO, Legal, or Procurement Clearance?
Our 100% in-RAM architecture removes the third-party processor from the sanitization path, reducing DPA negotiations, vendor risk questionnaires, and processor audits.