ZTDS™ RFC Standard

AI PII Redaction & Client-Side DLP for Prompts & DocumentsZero Cloud Egress. 100% RAM.

Sanitize sensitive customer PII, source code secrets, financial ledgers, and clinical records in local device RAM before sending to ChatGPT, Claude, Gemini, or Cursor. [FINANCIAL_DATA]

PII Sanitization Tool

STEP 1

Input

ZTDS™ VERIFIEDRAM:<1ms·0 B
Prompt:
Sample: HR / General
HIRING REVIEW > Candidate: Sarah Mitchell Email: s.mitchell@talent.io | Phone: +1 (415) 555-0182 Salary Expectation: $165,000.00 | SSN: 987-65-4321 Resume score: 94/100 — Shortlist for Senior Lead role.
Attach File (.docx, .xlsx, .pdf)
Upload documents (.pdf, .docx, .xlsx, .csv, .txt) or scan images with on-device OCR in RAM.
100% Offline
Paste Clipboard
Insert text from your clipboard directly into local RAM without saving to disk.
Instant Input
Custom Rules
Define your own detection rules to detect account numbers, internal codes, and custom PII patterns.
PRO Feature
AI NER (35MB)
Deep contextual NER model to detect complex names, organizations, and locations in RAM.
PRO Feature
0 / 15k
STEP 2

Sanitize Before AI

HIRING REVIEW > Candidate: [NAME_1]Sarah Mitchell Email: [EMAIL_1]s.mitchell@talent.io | Phone: [PHONE_1]+1 (415) 555-0182 Salary Expectation: [FINANCIAL_1]$165,000.00 | SSN: [ID_1]987-65-4321 Resume score: 94/100 — Shortlist for Senior Lead role.
STEP 4Paste AI Response → Reveal Original Data
Memory Standby
0 tokens in RAM
Test instant RAM reveal:
Encrypted team session handoff (TEAMS $99/mo)
Safe Copy Ready Prompt Copied! [NAME_1], [EMAIL_1] securely tokenized in local RAM.

"We run this before every ChatGPT session. Our InfoSec team was satisfied in one audit."

— Marcus T., Lead Compliance Engineer · European Fintech (400 employees)

"Finally — a PII tool that doesn't route my data through someone else's cloud."

— Jordan K., Senior DevOps Engineer · US Healthcare SaaS

"Used this to pass our SOC 2 AI-prompt review. The offline verification is the proof point."

— Priya N., Head of Legal Ops · Series B SaaS, 200 seats

Tailored Business Impact

Why Enterprises & Developers Choose Client-Side AI PII Sanitization

Eliminate prompt leakage at the physical layer. Whether closing enterprise AI software contracts, shielding corporate officers from regulatory penalties, or protecting sensitive client workpapers.

For AI SaaS & IntegratorsSales Enabler

Unlock Enterprise AI Deals

Stop losing high-ACV enterprise contracts to prospect InfoSec and DPO committees. Embed our zero-egress SDK into your AI workflows and arm sales teams with independent ZTDS Certificates of Conformance.

  • Accelerate vendor InfoSec & DPO reviews with verifiable 0-byte egress
  • Minimize subprocessor scope — direct PII is tokenized before cloud transmission
  • Standalone in-process Node/WASM SDK with <1ms linear execution latency
For CISOs & Corporate DPOsLegal Shield

Statutory Risk Minimization

Eliminate personal officer liability and statutory fines under GDPR Art. 83, EU AI Act, and CCPA/CPRA. Replace unenforceable employee guidelines with deterministic in-memory prompt tokenization.

  • Proactive Technical & Organizational Measures (TOMs) under GDPR Art. 32
  • 30 Specialized Profiles suppress narrative identifiers across tax, healthcare & legal
  • Downloadable SHA-256 cryptographic compliance receipts for statutory audits
For Legal, Finance & AdvisorySafe Productivity

Zero-Risk AI Productivity

Process client tax returns, settlement transcripts, and confidential contracts in ChatGPT or Claude without breaching professional ethics, NDA agreements, or statutory confidentiality.

  • 1-Click reverse de-tokenization restores original names and amounts in local RAM
  • Operates fully offline in Airplane Mode — zero telemetry and zero server logs
  • Visual PDF redaction & metadata purge for scanned tax and corporate filings
Regulatory Blueprints & Document Workflows

Sanitize High-Liability PDF, DOCX & Excel Documents Before Submitting to Enterprise AI Models

Eliminate PII, PHI, financial ledgers, and trade secrets in local RAM. Select your document type below for verified field-by-field redaction matrices and safe AI prompts.

GLBA • PCI DSS

Finance, Underwriting & Banking

Prevent customer account numbers, SWIFT MT103 instructions, and payroll records from leaking into training corpora.

Zero-Metadata .xlsx Export Finance Hub
FRE 502 • Privilege

Legal Counsel & Court Discovery

Preserve attorney-client privilege under Federal Rule of Evidence 502. Neutralize case numbers and party names.

100% In-RAM Rasterization Legal Hub
HIPAA • 18 Safe Harbor

Healthcare & Life Sciences

Comply with HIPAA 45 CFR § 164.514 Safe Harbor. Mask MRNs, patient names, and dates while preserving clinical symptoms.

HIPAA § 164.514 Safe Harbor (0 PHI Egress) Medical Hub
EEOC • GDPR

HR, Recruiting & Compensation

Conduct blind resume screening and salary benchmarking without injecting protected class identifiers or leaking payroll.

Anti-Bias Redaction HR Hub
SOC 2 • ISO 27001 • MCP

DevOps, Secrets & Autonomous AI Coding Agents

Protect internal API keys, database dumps, and cloud infrastructure secrets from entering LLM context windows in Cursor, Windsurf, Claude Code, and Copilot.

Stdio Local Streaming • 0ms Proxy Latency DevSecOps Hub
File-Level Deep Inspection • ZTDS Standard

Zero-Metadata Engine Breakdown: What PrivacyScrubber Strips Beyond Visible Text

Visual redaction alone leaves organizations exposed to court subpoenas and LLM data extraction. Real enterprise documents store deep internal XML structures, revision histories, and hidden text layers that cloud AI parsers automatically ingest.

3-Format Deep Dissection.DOCX / .XLSX XML.PDF Vector StreamOCR / EXIF Purge
.DOCX • .XLSX

OpenXML Package Dissection

Word and Excel files are ZIP archives storing internal XML trees. Naive text deletion leaves metadata intact.

docProps/core.xml & app.xml
Stripped: Author usernames, company name, revision count, total editing minutes, template lineage.
word/comments.xml & w:del
Stripped: Uncommitted track changes, reviewer feedback, and deleted text passages.
xl/workbook.xml & calcPr
Stripped: Cached formula values, hidden sheets, internal UNC network paths (\\corp-nas\payroll).
Clean OpenXML archive re-bundled in volatile RAM
.PDF (WASM)

Vector Stream & Text Layer Erasure

Court discovery exhibits and medical records demand the Anti-Manafort standard: 0 underlying text traces.

Tj & TJ Glyph Operator Streams
Obliterated: In Blackout mode, text operators are destroyed at the byte stream level, preventing clipboard extraction.
/Metadata & Info Dictionary
Stripped: Scanner serial numbers, printer GUIDs, PDF producer software, and embedded XML schemas.
Form Fields & JavaScript Streams
Purged: AcroForm interactive fields, annotations, embedded scripts, and hidden non-rendered PDF layers.
Court-proof: pdftotext returns 0 bytes under blackout
OCR • EXIF

Raster Burn-In & Hardware EXIF Purge

Mobile snapshots of driver licenses, invoices, and hospital intakes contain latent geolocation and hardware stamps.

EXIF / GPS / IPTC Metadata
Stripped: GPS coordinates (home/office latitude/longitude), camera model, device serial, timestamp.
Multimodal Burn-In Redaction
Overwritten: Solid blackout pixels or token badges are burned directly into bitmap canvas raster memory.
Zero Cloud Vision API
Zero-Egress: Local ZTDS™ offline OCR extracts bounding boxes in RAM. 0 bytes ever sent to cloud vision endpoints.
ExifTool clean • Safe buffer deallocation
CISO Verification MatrixAir-Gapped Standard Parity
File Security VectorLegacy / Cloud Redaction ToolsPrivacyScrubber ZTDS Engine
Visible PII Text (Names, SSNs, Accounts)Replaced visually on screenReplaced in-memory with reversible AI tokens or blackouts
Underlying PDF Text Layer (Anti-Manafort)Retained under black rectangles (extractable by AI)Physically destroyed from Tj/TJ vector streams
DOCX/XLSX Author & Company MetadataPreserved in docProps/core.xmlPurged 100% prior to native file export
Track Changes & Deleted CommentsStored in hidden XML revision tagsCompletely stripped from ZIP container
Camera EXIF & Smartphone GPS DataKept in image headers, leaking coordinatesEXIF dropped, raster burned in on HTML5 Canvas
Network Egress & Server StorageUploaded to remote cloud proxy / API server0 bytes sent to network • 100% in local RAM (Airplane Mode)
In-RAM Document Sanitizers

Direct File Format Engines (Zero Cloud Upload)

Institutional Proof of Due Diligence

Cryptographic PII Audit Receipts & A4 Certificate of Conformance

Every deployed PrivacyScrubber engine produces legally authoritative documentation. Export vector-crisp, printable A4 PDF certificates signed under the Zero-Trust Data Sanitization standard (ZTDS RFC v1.0) to satisfy internal compliance audits, GDPR Data Protection Impact Assessments (DPIAs), and enterprise customer security reviews.

View Live Verification & PDF →Offline verifiable via WebCrypto Ed25519
RFC v1.0 Valid
ZTDS CONFORMANCE
Standard Seal
Target:privacyscrubber-web
Egress Guarantee:0 BYTES (RAM-ONLY)
Legal Standard:GDPR Art. 32 / TOMs
Audit Receipt:SHA-256 Verified
Attestation:Ed25519 Signed
Printable A4 PDF Verify Entity →
Evidentiary Sovereignty Manifesto

Client-Side RAM Sanitization vs. Cloud DLP Proxies: Paper Promises vs Physical Data Sovereignty

Not your RAM, not your data. The fundamental divide between signing legal contracts to allocate post-breach liability versus enforcing mathematical zero-egress before generative models ever see raw text.

Model A: Cloud Paper Compliancevs.Model B: Physical Data Sovereignty (ZTDS™)
Model A • Legacy Cloud Security

Paper Compliance

Post-Breach Liability

Organizations rely on Data Processing Agreements (DPAs), Business Associate Agreements (BAAs), and trust declarations from cloud proxy vendors (Skyflow, Presidio Cloud, AWS Comprehend).

Continuous Third-Party Egress

Unredacted prompt text, client IDs, and financial records transit across external fiber cables to intermediary vendor cloud servers.

Residual Cloud Custody & Subpoena Risk

Ephemeral cloud caches, server crash logs, and worker heaps remain vulnerable to insider threats, infrastructure compromises, and CLOUD Act warrants.

Procurement Drag (6–8 Weeks)

Requires exhaustive InfoSec supplier questionnaires, subprocessor chain audits, and legal review of third-party indemnification caps.

Reactive Financial Exposure

When a cloud subprocessor leaks, the DPA only defines who pays the lawyers. Average IBM Cost of a Data Breach: $4.88M.

Operational Stance: Trust Promises • Sue Post-Breach
Model B • ZTDS™ Open Standard

Physical Data Sovereignty

Zero Egress Isolation

Organizations rely on deterministic CPU tokenization isolated in local workstation RAM (IETF draft-sibiryakov-ztds-protocol).

Strict Zero-Byte Network Transmission

Raw text never hits the network adapter. All tokenization, entity verification, and redactions complete inside browser V8 RAM in <2ms.

Physical Isolation Against Subpoena & Leaks

No cloud server holds your cleartext session map. It is mathematically impossible to breach, leak, or subpoena data that was never transmitted.

0-Day Procurement (GDPR Art. 28 Subprocessor Path Eliminated)

Because exactly 0.00 bytes of personal data leave client RAM, PrivacyScrubber is not a Data Processor under GDPR Art. 4(8) or HIPAA. InfoSec and Legal grant immediate clearance without 6-week vendor delays.

Empirical Verification (Airplane Mode)

Fully functional with Wi-Fi disabled. Inspect Chrome DevTools Network tab: exactly 0 requests and 0 bytes transferred.

Deep Zero-Metadata Office Sanitization

Beyond visible text, our in-RAM engine purges hidden XML properties (docProps/core.xml, wb.Props), wiping authors, corporate tags, and revision history in DOCX and XLSX before download.

Operational Stance: Mathematical Proof • Hardware Isolation
The 2026 Irreversibility Trap • EU AI Act Article 10

Why Data Deletion from Frontier LLMs is Impossible

Once sensitive data enters an AI model or enterprise RAG vector store, it cannot be selectively deleted—machine unlearning remains unsolved. Network gateway DLPs miss encrypted WebSockets and streaming SSE tokens. PrivacyScrubber enforces source-level sanitization in local RAM before transmission, satisfying EU AI Act governance and DORA resilience mandates.

In-DOM AI Gateway

Sanitize AI Prompts Before They Leave Your Browser In-Page Real-Time Protection on ChatGPT, Claude & Gemini

Automatically detect and tokenize customer names, API keys, medical notes, and financial data directly inside your AI chat window. 0ms network latency — 100% local browser RAM processing.

Desktop AI Shield
★ 5.0 CWS

Zero-exfiltration prompt sanitization directly in your AI chat window

Intercepts names, emails, cards, and keys in local RAM before prompt transmission to LLMs. Zero server logs.

ChatGPT Claude Gemini Copilot DeepSeek
Desktop AI Shield · MV3

In-Page Prompt Sanitizer for ChatGPT, Claude & Gemini

Air-gapped client-side interception inside your AI text inputs. Customer identities, credentials, medical notes, and financial records are sanitized in local RAM before prompt transmission.

In-Page Auto-Detection (9 LLMs)

Native injectors for ChatGPT, Claude, Gemini, Copilot, DeepSeek, Perplexity, Poe, HuggingFace, and Mistral.

1-Click Reverse Reveal in Chat

Instantly swaps tokens in the AI response back to original names and data directly in your browser.

100% Offline RAM & ZTDS Receipts

30 industry profiles (HIPAA, GDPR), custom regex rules, and cryptographic audit receipts with zero server telemetry.

Add to Chrome — Free (★ 5.0 CWS)
Free Forever · Installs in 5sArchitecture & Docs
Manifest V3
0-Byte Egress
Local RAM (<1ms)
★ 5.0 CWS Rated
gemini.google.com
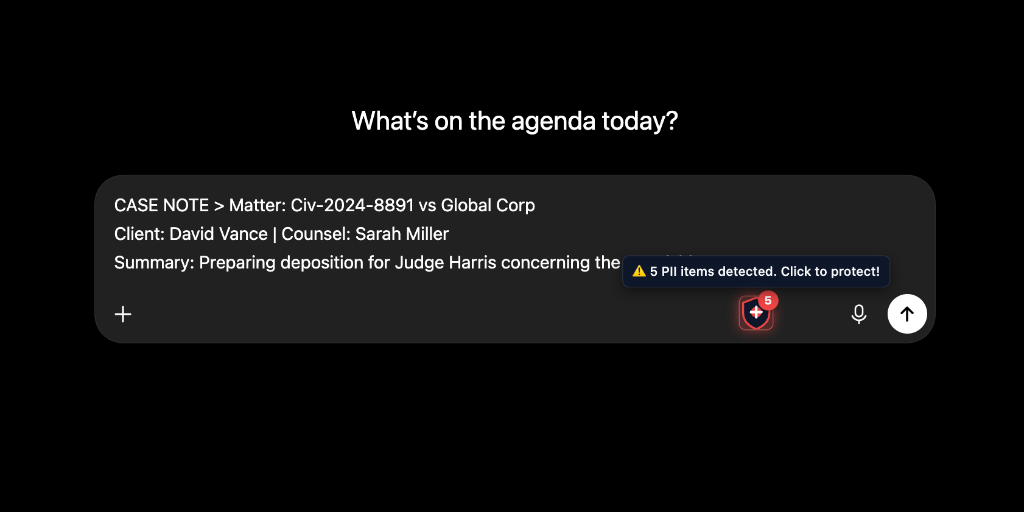
PrivacyScrubber detects sensitive items in the prompt

Step 1: Detection

Step 1 of 4

Type or paste your text normally. The extension instantly detects sensitive data like names, emails, or IDs right inside the text box.

Zero-Trust Industry Architecture

How Teams in Finance, Healthcare & Legal Remove PII Before AI

See how PrivacyScrubber anonymizes data for each industry — step by step. Every action runs in local browser RAM with zero server contact.

Risk: Hardcoded Secrets & DB DumpsAvg Breach: $4.9MTarget: In-Process SDK & MCP

In-Process Interception: APIs, DB Dumps & RAG Vector Lakes

Developers and AI agents pipe crash dumps and customer records into LLMs, leaking AWS credentials, JWTs, and consumer PII. The Developer SDK and MCP Server act as an autonomous consumer privacy fiduciary—intercepting sensitive entities at the application boundary in <1ms local RAM before transmission, vector indexing, or logging.

devops_crash_log.log
// Raw text pasted into Cursor/ChatGPT
Error connecting to DB: postgres://admin:superSecretPass2026@prod-db.internal:5432/customers
AWS_KEY: AKIA4X9M2PLRT887NNZZ
// Tokenized in client RAM with Zero Network Transmission
Error connecting to DB: postgres://admin:[PASSWORD_1]@prod-db.internal:5432/customers
AWS_KEY: [API_KEY_1]
// 1-Click Reveal rehydrates original DB credentials on your machine
LLM Solution: Fix connection pooling for postgres://admin:superSecretPass2026@...
"Security analysts tokenize IP addresses, credentials, and hostnames from incident logs locally before running AI root-cause analysis — zero data exposure to cloud APIs."— OSCP Security Analyst • Cloud Infrastructure Team
Risk: PCI-DSS v4.0 & GLBAPenalties: Up to $100k/moTarget: Extension & Web

Zero-Server Sanitization for PAN, IBAN & Wire Transfers

Financial analysts modeling client portfolios or summarizing bank statements risk exposing primary account numbers (PAN) and SWIFT codes. PrivacyScrubber uses deterministic PCI sanitization locally in RAM before transmission.

wire_instruction.txt
// Sensitive wire transfer pasted for LLM review
Wire $450,000.00 to Robert Chen (Acct: 4532-0151-8879-2241, IBAN: US948123490019283, SSN: 203-44-8821).
// Deterministic PAN sanitization with contextual token consistency
Wire [FINANCIAL_1] to [NAME_1] (Acct: [CARD_1], IBAN: [IBAN_1], SSN: [SSN_1]).
// AI generates audit memo → Reveal rehydrates real numbers locally
LLM Audit Report: Verified authorization for Robert Chen ($450,000.00) with Goldman Sachs.
"GRC teams sanitize financial reports and operational files offline before AI-powered audit prep — no vendor database storage, no scope extension for external auditors."— Fintech GRC Team • SOC 2 & ISO 27001 Readiness
Explore Financial Compliance
Risk: HIPAA 18 IdentifiersStatutory Fine: $1.9MSafe Harbor Certified

De-Identify EHR Notes & Clinical Diagnostics

Physicians and clinicians summarize EHR records and patient histories without waiting months for signed BAA agreements. PrivacyScrubber implements the HIPAA Safe Harbor standard 100% in local browser RAM.

clinical_chart_ehr.txt
// Unredacted clinical chart
Patient: Sarah Jenkins (DOB: 1984-05-12, SSN: 042-88-9124). Admitted for acute bronchitis. Primary: Dr. Gregory House. Policy #BC-99214.
// 18 HIPAA identifiers tokenized locally in RAM
Patient: [NAME_1] (DOB: [DATE_1], SSN: [SSN_1]). Admitted for acute bronchitis. Primary: [DOCTOR_1]. Policy [POLICY_1].
// AI generates diagnostic plan → Reveal rehydrates patient identity locally
Clinical Care Summary: Recommended antibiotic dosage plan for Sarah Jenkins under care of Dr. Gregory House.
"Clinical teams strip all 18 HIPAA Safe Harbor identifiers from patient notes in browser RAM before using AI summarization — transforms PHI into Safe Harbor de-identified tokens in local browser RAM before transmission."— Clinical Informatics • PHI De-Identification
Risk: EEOC Bias & Candidate PIIGDPR Employee DataTarget: Batch CSV / DOCX

Blind Resume Screening & Bulk Salary Anonymization

HR practitioners analyzing payroll compensation or screening resumes risk leaking salaries and introducing gender/racial bias into AI models. Bulk offline file processing strips identifiers before AI analysis.

candidate_screening.csv
// Candidate resume and compensation history
Candidate: Emily Watson (Email: emily.w@enterprise-tech.io, Salary: $165,000/yr, SSN: 019-48-2910).
// Anonymized profile for bias-free LLM skill evaluation
Candidate: [CANDIDATE_1] (Email: [EMAIL_1], Salary: [SALARY_1], SSN: [SSN_1]).
// AI produces skill ranking → Reveal rehydrates contact details locally
Unbiased Assessment: Candidate Emily Watson meets all L6 Engineering leadership qualifications.
"HR teams batch-anonymize resumes and compensation tables in local memory before feeding to LLMs for skill evaluation — eliminating unconscious gender/ethnic bias and protecting employee GDPR rights."— Head of People Ops • Enterprise Talent Acquisition
Bulk File Sanitizer (PRO)
Architecture: Two-Tier Fleet GovernanceISO 27001 & SOC 2Teams Hub ($99/mo)

Two-Tier Fleet Governance: Central CISO Lock + Local Flexibility

Employees will use generative AI regardless of corporate bans. PrivacyScrubber solves the Shadow AI paradox through a two-tier architecture: Central security officers enforce mandatory regex rules, while employees retain local agility.

Tier 1: Central CISO Hard Lock
Deploy non-negotiable MDM regex rules via Chrome Enterprise. Mandates zero-tolerance blocking for PAN, SSN, API secrets, and proprietary project codes across every managed browser.
Tier 2: Local Worker Agility
Engineers and analysts create ad-hoc local sanitization rules for active client projects on the fly, eliminating IT friction and helpdesk change tickets.
Encrypted Handoff via XChaCha20-Poly1305 + Argon2id
Zero-Knowledge Guarantee
"VP InfoSec teams deploy locked Team Blueprints that enforce identical sanitization profiles across 500+ employees — preventing shadow AI data leaks organization-wide."— VP InfoSec & CISO • Enterprise AI Governance
·CISO Blueprint
Verifiable Zero-Trust & Regulatory Coverage

Verify Zero Data Egress in 60s & Technical Safeguards for GDPR, HIPAA, SOC 2 & EU AI Act

No auditor or vendor trust needed. Open DevTools to prove PrivacyScrubber sends zero network requests with your data — backed by turnkey statutory compliance for enterprise LLM deployments.

60-Second Proof of Zero Transmission

Independent DevTools verification protocol for InfoSec & SecOps (0 requests · 0 B transferred)

Airplane Mode Verified
Inspect Steps
1
Open DevTools

Press F12 or right-click → Inspect

2
Network Tab → Clear

Click the Clear icon to reset active request log

3
Airplane Mode (opt)

Cut Wi-Fi — engine runs 100% offline

4
Paste → Protect

Watch Network tab as text is tokenized

5
Audit Result: 0 Network Requests with PIIVerified

Zero bytes egressed to external endpoints — verified zero egress by architecture.

Network:0 requests|0 B transferred
Architectural Objection Defense

6 Tough Questions Security Architects Ask Us

Direct technical answers addressing the core questions evaluated by CISOs, security researchers, and enterprise review committees.

01Why not Presidio or cloud NER models?
Cloud NER sends raw text to remote servers, violating Zero-Trust before masking occurs. ZTDS™ executes deterministic entity tokenization locally in RAM (<1ms) with zero cloud leaks.
Deterministic RAM Engine · 0ms Network Hops
02How is browser memory protected from extraction?
PrivacyScrubber operates under strict CSP (script-src 'self') with zero external scripts. The volatile ZTDS™ token dictionary is strictly tab-isolated, never stored on disk or cookies, and wiped on tab close.
Volatile V8 Heap · Zero Persistence
03What happens if generative AI alters synthetic tokens?
Our patent-pending engine uses deterministic ZTDS™ token restoration to handle model case changes, whitespace shifts, and markdown styling. Omitted tokens are flagged in the local audit log without corrupting text.
ZTDS™ Token Restoration · U.S. & Int'l Patents Pending
04How does InfoSec audit compliance without central servers?
PrivacyScrubber generates cryptographically verifiable CISO receipts (SHA-256 hash, entity count) directly on-device. Enterprise teams stream zero-PII telemetry locally to internal SIEMs (Splunk, Datadog) via our Node.js SDK and MCP.
Local SHA-256 Proof · Zero-PII SIEM Webhooks
05Why use ZTDS if our enterprise signed an Azure OpenAI or ChatGPT Enterprise BAA?
Enterprise BAAs and DPAs establish who pays the lawyers and regulatory fines after an incident, but they cannot prevent raw customer IDs, trade secrets, and API keys from landing in cloud provider crash logs or being reached via CLOUD Act subpoenas. A paper contract protects legal counsel during discovery; physical ZTDS ensures the data was never transmitted in the first place.
Technical Safeguard vs Paper-Only Controls • Not Your RAM, Not Your Data
06What if our documents contain rare or proprietary PII?
Beyond 30 pre-built industry profiles, users and admins can define custom client-side regular expressions or import MDM-locked company dictionaries that execute 100% locally in device memory.
30 Profiles · Custom Regex · MDM Policy Lock
Architecture Benchmark

Paper Contracts vs Technical Safeguards: Local RAM vs Cloud DLP

Sign a DPA to allocate liability after an incident, or isolate memory so a breach is physically impossible. Why enterprise security architects choose in-memory client-side ZTDS over cloud DLP proxies.

Compare Matrix

Cloud DLP Proxies & Gateways

High Overhead
  • Network Egress: Transmits unredacted prompt payloads over the internet to intermediate cloud proxy servers.
  • High Latency: 250ms – 600ms latency penalty per AI query due to multi-tenant cloud roundtrips.
  • Probabilistic NLP: Cloud LLM redactions risk hallucinating tokens, skipping entities, or rewriting prompt semantics.
  • Procurement Overhead: Requires 6–8 week legal reviews, BAAs, DPAs, and third-party vendor risk questionnaires.

PrivacyScrubber Client-Side ZTDS

Zero Risk
  • 0-Byte Transmission: 100% volatile local RAM processing. Fully functional offline in Airplane Mode.
  • Sub-2ms Latency: Near-zero latency overhead (<2ms local CPU tokenization). Zero network queues.
  • Deterministic Precision: Rigorous deterministic pattern engines. Zero token hallucinations.
  • Statutory Safe Harbor: Zero-processor architecture clears DPO reviews in 48 hours without third-party DPA gridlocks.
Sub-2ms In-Memory

100% reproducible RAM tokenization

30 Industry Profiles

HIPAA Safe Harbor, GDPR, PCI DSS

Custom Regex & WASM OCR

Air-gapped scanned PDF processing

6 Global Statutory Frameworks · 0 Payload Packets · Zero Subprocessors
Zero-Trust Data Sanitization (ZTDS) · Zero Per-Seat Tax

AI PII Redaction & Data Sanitization Pricing. Zero Per-Seat Tax.

Sanitize sensitive prompts, PDFs, and spreadsheets 100% locally in browser RAM before sending to ChatGPT, Claude, Gemini, or Cursor. Compare Free, PRO ($15/mo or $110 Lifetime), flat-rate Teams ($99/mo for unlimited seats), and in-process Node.js/WASM Developer SDK ($299/mo) plans — supporting GDPR Art. 32, HIPAA & SOC 2 technical safeguards with zero subprocessor risk.

Zero Accounts•Offline Cryptographic Key•100% In-Browser RAM
Swipe cards or tap arrows 1 of 4 · Free
Community Tier · Free Forever
$0/ forever
Free quota across all 4 environments · Zero accounts or logins required
4 Free EnvironmentsFree Quota
Scrub Prompts Free (15,000 Chars)
15k Chars Free•Zero Accounts•100% RAM-Only
PRO Tier · Individual Safe Harbor
$15/ mo
For solo practitioners, lawyers & devs · $110 Lifetime
Unlimited Personal3 Devices
Sample Audit PDF
Instant Key•Up to 3 Devices•Cancel Anytime
Best Value
TEAMS Plan · Dept Security
$99/ mo flat
Domain-wide protection for law firms, clinics & enterprise teams
Company Domain FleetFlat Rate
Unlimited Seats•Instant Key•No Per-User Tax
Developer SDK · OEM
In-Process
$299/ mo
Free dev quota · $299/mo or $2,990/yr for unlimited production nodes
Free Local Quota
Free Dev Quota•<0.4ms In-Process•$2,990/yr Option
44,000x Liability Mitigation Asymmetry

AI Data Breach Cost vs. Cloud DLP vs. Client-Side ZTDS™ Pricing

Zero Subprocessors · Zero Data Egress
Swipe to compare risk vs solution 1 of 3 · Breach Cost
Cost of Inaction
$4,880,000

Average cost of a GenAI corporate data breach according to the IBM Security Report.

  • Up to €20M or 4% turnover (GDPR & EU AI Act Art. 50).
  • $50,000/violation statutory HIPAA willful neglect fines.
  • 6–12 week enterprise procurement stalling for vendor reviews.
Verdict: Catastrophic Downside
In-House DIY Trap
$50,000+/yr

Internal engineering salary to build, test and maintain custom regex DLP logic.

  • $500–$2,000/mo server bills for centralized cloud proxy nodes.
  • 200–500ms network roundtrip latency on every developer prompt.
  • Ongoing regex drift, edge-case false positives & triage drag.
Verdict: High Maintenance Drag
Zero-Trust Protocol (ZTDS™)
$99/mo flat

Flat-rate team protection with 100% in-memory client-side sanitization.

  • 0-Day Approval: Zero subprocessors in the sanitization path, less DPA paperwork.
  • <2ms local RAM execution with 0 bytes network egress.
  • Turnkey compliance proofs: SOC 2 Type II & ISO 27001 mapping.
Verdict: Pure Mathematical Asymmetry
Zero-Database Architecture

Offline Cryptographic Licensing: Zero Accounts & Air-Gapped Activation

We refuse to store your passwords or track your identity in a central database. Privacy is an engineering guarantee, not a marketing promise.

1. Zero Accounts & No Passwords

You never create an account, set a password, or trust us with login credentials. There is no cloud user database to be breached, scraped, or subpoenaed.

0 Credentials Stored • 100% Anonymous

2. Offline Cryptographic Keys

Paid tiers (PRO, TEAMS, SDK) activate via an offline cryptographic license key. Validation occurs mathematically in your local RAM without cloud telemetry or pingbacks.

Airplane Mode Verified • Zero Pingbacks
Procurement & CISO Total Cost of Ownership (TCO)

Traditional Cloud DLP vs. PrivacyScrubber TEAMS — 94% Cost Reduction

Cloud DLP vendors charge $30–$50/user/mo ($18,000–$30,000/yr for 50 seats), introduce 250ms+ network latency, and require months of vendor security assessments. PrivacyScrubber TEAMS costs $99/mo flat ($1,188/yr) for unlimited seats with zero server-side subprocessor liability.

Annual Savings
$16,800+ / yr
Air-Gapped Enterprise & Source Code EscrowCustom SLA

Complete on-premise source code licensing, 100% air-gapped sovereign deployment, proprietary patent-pending architecture (U.S. & Int'l Patents Pending), custom SIEM log integration, dedicated GRC support & bilateral DPA for healthcare systems, banks, defense, and large multi-seat organizations.

Talk to Enterprise
What You Get & Why It Matters

Role & feature entitlements across Free, PRO, TEAMS, and Enterprise tiers

Compare All Specifications →
Module & FeatureOutcome & Problem SolvedWho Uses ItTiers
In-Page Chrome Shield Sanitizes prompts right inside ChatGPT, Claude, and Gemini with hotkey Alt+Shift+X without switching tabs. All AI Users & AnalystsFree (15k) / PRO / TEAMS
30 Industry PII Profiles Pre-configured detection for HIPAA health data, legal court filings, IBAN bank numbers, and payroll records. Doctors, Lawyers, AccountantsPRO & Above
IDE MCP Server (stdio) Strips database credentials, JWTs, and secret tokens before Cursor or Claude Code AI agents read your source repository. Free with session quota. Software Engineers, DevOpsFree (Quota) / PRO / TEAMS
Offline PDF & OCR Extracts and sanitizes scanned contracts and screenshots in volatile RAM without sending images to cloud vision APIs. Legal, HR, ProcurementPRO & Above
Excel & CSV Cell Scrub Cell-by-cell PII sanitization in local memory preserving formulas, spreadsheet structures, and numeric salary sums. Data Analysts, UnderwritersPRO & Above
Zero-Metadata File Stripping Physically strips OpenXML revisions (w:del), hidden comments, calcPr UNC paths, PDF Tj/TJ vector streams, and EXIF stamps. Lawyers, Auditors, HR, CISOsPRO & Above
Custom Regex & Secrets Custom regex builder to sanitize proprietary internal project codenames, custom customer IDs, and API secrets. Security Engineers, R&DPRO & Above
1-Click Reverse Reveal Instant local rehydration restoring real customer names and parameters into AI responses inside browser memory. Support, Sales, RecruitersFree / PRO / TEAMS
Zero-Knowledge Session Handoff Securely transfer sanitized AI prompt sessions to colleagues via encrypted P2P links without storing data in any central server database. Cross-functional TeamsTEAMS & Above
Central Rules & Policy Governance Distribute company-wide PII policies, proprietary codenames, and custom regex across employee browsers with zero server sync. Security Officers, IT DirectorsTEAMS & Above
Cryptographic Audit Receipts 1-click signed PDF certificate with SHA-256 session hashes proving zero confidential data left your premises. Compliance Officers, DPOsPRO & TEAMS
Developer SDK & CLI In-process consumer privacy fiduciary (@privacyscrubber/sdk) embedded into Node.js / WASM. Pre-emptively intercepts PII at the application boundary with zero data loss, zero third-party DLP proxies, and <1ms execution before vector indexing or LLM egress. Backend Developers, AI Engineers, RAG ArchitectsFree (Quota) / $299 Prod
License Custody & Kill Switch
Zero-server key custody with instant emergency revocation (KRL) if a key is leaked. Master Admin Key isolation for teams. All License Holders, CISOsAll Paid Tiers
Air-Gapped RAM Operation Verified 0-byte outbound network egress in Airplane Mode, bypassing DPAs and third-party vendor audits. CISOs, Defense, BanksAll Tiers
Accepted Payment Methods
Wire / Invoice
PCI-DSS Compliant · 30-Day Refund
Full Pricing & ROI Calculator
Answers & Security FAQ

Client-Side AI Privacy & PII Sanitization FAQ

Everything you need to know about browser-based PII redaction, compliance scope, and AI safety.

Verified architecture & compliance answers
Security & ZTDSDoes PrivacyScrubber send my text, documents, or meeting transcripts to any server?
No. Every detection and sanitization operation runs 100% locally inside your browser's RAM. Zero bytes of your text, documents (.pdf, .docx, .xlsx, .txt), or meeting transcripts ever leave your workstation. The entire application operates like a self-contained local utility: file parsing, text extraction, and PII redaction execute exclusively in local memory. You can verify this complete data isolation by disconnecting your internet (Airplane Mode) or opening DevTools → Network tab: PrivacyScrubber continues sanitizing with 100% functionality and zero network requests.
Security & ZTDSWhat is AI DLP and how does client-side browser sanitization differ from a legacy cloud proxy?
AI Data Loss Prevention (AI DLP) refers to specialized security controls engineered to inspect and sanitize unstructured conversational prompts, streaming tokens, and file uploads before ingestion by generative AI models. Traditional gateway DLPs (like Zscaler, Netskope, or Cloudflare proxies) sit downstream in the network and struggle with encrypted WebSockets, streaming Server-Sent Events (SSE), and conversational context—often causing latency or failing to de-identify data before transit. PrivacyScrubber executes AI DLP directly at the source: inside local browser RAM (<2ms latency). Sensitive entities are converted into contextual tokens ([NAME_1], [ACCOUNT_1]) before packets ever reach the network adapter, guaranteeing zero vendor data custody and physical isolation from cloud data egress.
Compliance & LegalWhat is the AI data irreversibility problem and why must PII redaction happen at the client endpoint?
The AI Irreversibility Problem stems from the mathematical impossibility of selectively 'unlearning' or excising data once it has been digested into large language model neural weights or stored in multi-tenant RAG (Retrieval-Augmented Generation) vector databases. Machine unlearning remains an unsolved scientific challenge; post-hoc deletion requests (such as GDPR Article 17 'Right to be Forgotten') cannot be reliably enforced against fine-tuned weights or vector embeddings. Consequently, regulatory bodies (under the EU AI Act Article 10 and HIPAA Safe Harbor) require data sanitization to occur strictly prior to ingestion. PrivacyScrubber's endpoint-only RAM architecture guarantees that sensitive identifiers never enter LLM training corpora or remote vector caches.
Security & ZTDSHow does PrivacyScrubber prevent data residue and protect browser heap memory?
PrivacyScrubber maintains zero data residue through a defense-in-depth memory architecture: After processing documents (PDF, DOCX, XLSX), the engine immediately zeroes all temporary ArrayBuffers inside volatile ZTDS™ browser RAM immediately upon completion. Session maps are strictly tab-isolated, never written to disk, cookies, or browser storage, and are permanently wiped on tab close. Strict Content Security Policy (script-src 'self') with zero third-party analytics prevents DOM and memory scraping. In-memory heap profiling enforces an ultra-lightweight ceiling under 6MB RAM (5.68 MB JS Heap) with sub-75ms streaming mutation scans.
Security & ZTDSWhy deterministic regex rules instead of cloud NER models like Microsoft Presidio or BERT?
Sending sensitive text to remote Named Entity Recognition (NER) models leaks raw data before masking can occur. ZTDS executes deterministic contextual pattern regular expressions and 30 specialized industry vocabularies 100% locally in device memory (<1ms latency), providing 100% reproducible compliance proofs without stochastic AI hallucinations, entity omissions, or model drift.
Compliance & LegalDoes PrivacyScrubber support HIPAA, GDPR, and SOC 2 de-identification?
PrivacyScrubber is engineered for statutory risk minimization and technical safe harbor under HIPAA Safe Harbor (45 CFR §164.514) for 18 PHI identifiers, GDPR Article 25/32 data minimization, and SOC 2 Type II controls by stripping identifiers in browser RAM before prompt submission. Review our Top 20 Corporate PII Guide and CISO AI Security Blueprint for detailed governance controls.
Compliance & LegalWhy is a Data Processing Agreement (DPA) or BAA not required, and how does the CISO Memo bypass procurement delays?
Under GDPR Article 4(8)/Article 28 and HIPAA 45 CFR § 164.502(e), DPAs and BAAs are legally required only when an external vendor processes or stores protected data on remote cloud infrastructure on your behalf. Because PrivacyScrubber executes 100% in local client-side RAM with zero server data transmissions and zero subprocessors, PrivacyScrubber is legally classified as an autonomous software vendor rather than a data processor. Our standardized CISO Procurement Memo provides General Counsel and DPOs with statutory evidence, eliminating lengthy vendor risk questionnaires (SIG/CAIQ) and enabling fast-track 0-day software approval.
Compliance & LegalWhy do organizations need ZTDS if they already have Azure OpenAI or ChatGPT Enterprise with a BAA?
Business Associate Agreements (BAAs) provide contractual recourse after a security incident, not physical leak prevention. They do not prevent cloud logging misconfigurations, insider access, prompt injection exploits, or US CLOUD Act data subpoenas. Data that never leaves the workstation in the first place cannot be breached, inspected, or subpoenaed.
Enterprise Knowledge Base

Need More Technical, Compliance, or Architecture Answers?

Explore our complete 45-question Knowledge Base covering HIPAA BAA exemptions, offline OCR raster flattening, Node.js SDK streaming, and air-gapped MCP stdio integration.

Browse All 45 FAQ Answers
Zero-Vendor-Risk Clearance

Need CISO, Legal, or Procurement Clearance?

Our 100% in-RAM architecture removes the third-party processor from the sanitization path, reducing DPA negotiations, vendor risk questionnaires, and processor audits.